> For the complete documentation index, see [llms.txt](https://docs.enginsight.com/docs/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://docs.enginsight.com/docs/manual/english/platform-usage/hosts/management/policy-manager/add-policy-manager.md).

# Add Policy Manager

<i class="fa-computer-mouse">:computer-mouse:</i> Click <i class="fa-plus">:plus:</i> **Create Policy** in the upper-right corner of the [policy manager overview](file:///#policy-manager-overview) and select one of the following options from the submenu that opens:

* [Create New](#general-settings): Select this option if you want to create a new policy manager.
* [Import](#import-policy-managers): Select this option if you want to import one or more policy managers that you previously exported, for example from other organizations.

***

## Creating a New Policy Manager

<i class="fa-computer-mouse">:computer-mouse:</i> Click <i class="fa-plus">:plus:</i> **Create Policy** in the upper-right corner of the [policy manager overview](file:///#policy-manager-overview) and select **Create New** from the submenu that opens to add a new policy manager.

<figure><img src="https://2423388680-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FV7OrHgKXA0t1jankQBYf%2Fuploads%2Fgf0t0Bso0TXfRVqw8sjO%2FEnginsight-EN-Hosts-Add%20Policy-Full.jpg?alt=media&amp;token=c35c7fdb-dd5d-4f7d-9500-b19b27b3e0ee" alt=""><figcaption></figcaption></figure>

<i class="fa-computer-mouse">:computer-mouse:</i> Click **Create Policy** after configuring all settings to save and create the new policy.

<i class="fa-computer-mouse">:computer-mouse:</i> Click **Back** to return to the overview.

{% hint style="danger" %}
**Please note:** If you leave this view without clicking **Create Policy**, all configured settings will be lost permanently.
{% endhint %}

***

## General Settings

Here you can configure various basic settings.

<figure><img src="https://2423388680-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FV7OrHgKXA0t1jankQBYf%2Fuploads%2FuOf1q4unV7NYm8PTrbMi%2FEnginsight-EN-Hosts-Add%20Policy-General%20Settings.jpg?alt=media&amp;token=0406c081-ca78-41f1-81b4-8e656482795c" alt=""><figcaption></figcaption></figure>

The following options are available:

<table><thead><tr><th width="200.47265625">Option</th><th>Description</th></tr></thead><tbody><tr><td>Name</td><td>Enter a meaningful name for the policy.</td></tr><tr><td>Description</td><td><p> Provide a more detailed description of the policy. </p><div data-gb-custom-block data-tag="hint" data-style="info" class="hint hint-info"><p>This field is optional</p></div></td></tr><tr><td>Priority</td><td><p>Define a priority between <strong>1</strong> and <strong>100</strong> for the policy.</p><div data-gb-custom-block data-tag="hint" data-style="info" class="hint hint-info"><p>The default priority is <strong>50</strong>.</p></div><div data-gb-custom-block data-tag="hint" data-style="warning" class="hint hint-warning"><p><strong>Please note:</strong> If multiple policies are assigned to the same host, the policy with the higher priority is applied.</p></div></td></tr></tbody></table>

## Assigned Hosts

{% hint style="danger" %}
**Please note:** A policy overrides the [settings of all assigned hosts](/docs/manual/english/platform-usage/host-detail-view/settings.md#core-feature). If you do not want the settings of specific hosts to be overwritten, you can [exclude these hosts from the policy](#excluded-hosts).
{% endhint %}

Here you can define the hosts or groups of hosts to which the configured settings should apply.

<div align="left"><figure><img src="https://2423388680-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FV7OrHgKXA0t1jankQBYf%2Fuploads%2FYR7UyXLPL5lH4nfJExPa%2FEnginsight-EN-Assigned%20References.jpg?alt=media&amp;token=cebf4535-0c6c-4404-a071-76821b8fc228" alt=""><figcaption></figcaption></figure></div>

The following options are available:

<table><thead><tr><th width="199.625">Option</th><th>Description</th></tr></thead><tbody><tr><td>Hosts</td><td><p>Define the hosts to which the configured settings should apply.</p><p></p><p><i class="fa-computer-mouse">:computer-mouse:</i> Click the <strong>Hosts</strong> field to expand a list of all available hosts, then select one or more hosts. Alternatively, use the free-text search to find hosts in the list more quickly.<br></p><p><i class="fa-computer-mouse">:computer-mouse:</i> Click the <strong>Remove</strong> icon <i class="fa-circle-xmark">:circle-xmark:</i> next to an added host to remove it from the <strong>Hosts</strong> field.</p></td></tr><tr><td>Tag Logic</td><td><p>Define how many tags an assigned host must have for the settings to apply to it.</p><div data-gb-custom-block data-tag="hint" data-style="info" class="hint hint-info"><p>The default tag logic is <strong>All Tags are Present in the Reference</strong>.</p></div><p><i class="fa-computer-mouse">:computer-mouse:</i> Click the <strong>Tag Logic</strong> field to expand a list of all available options.<br><br>The following options are available:</p><ul><li><strong>All Tags are Present in the Reference:</strong> An assigned host must have all specified tags for the settings to apply to it.</li><li><strong>At Least One of the Specified Tags is Present:</strong> An assigned host must have at least one of the specified tags for the settings to apply to it.</li></ul></td></tr><tr><td>Tags</td><td><p>Define tags for groups of hosts to which the configured settings should apply.</p><p></p><p><i class="fa-computer-mouse">:computer-mouse:</i> Click the <strong>Tags</strong> field to expand a list of all available tags, then select one or more tags. Alternatively, use the free-text search to find tags in the list more quickly.<br></p><p><i class="fa-computer-mouse">:computer-mouse:</i> Click the <strong>Remove</strong> icon <i class="fa-circle-xmark">:circle-xmark:</i> next to an added tag to remove it from the <strong>Tags</strong> field.</p></td></tr></tbody></table>

### Excluded Hosts

Here you can define which hosts or groups of hosts should be explicitly excluded from the configured settings.

{% hint style="info" %}
Defining excluded hosts is optional.
{% endhint %}

<i class="fa-computer-mouse">:computer-mouse:</i> Click <i class="fa-plus">:plus:</i> **Define Exceptions** next to **Assigned Hosts** to show the options for **Excluded Hosts**.

<div align="left"><figure><img src="https://2423388680-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FV7OrHgKXA0t1jankQBYf%2Fuploads%2FOwkoC0RXeV3yJg6fqoh0%2FEnginsight-EN-Excluded%20References.jpg?alt=media&amp;token=25189e42-a39b-4936-a80a-3780807e258f" alt=""><figcaption></figcaption></figure></div>

<i class="fa-gear">:gear:</i> Configure all settings as described for an assigned host.

***

## Available Settings

Here you can define the exact settings that should apply to all hosts assigned to the policy manager.

<div align="left"><figure><img src="https://2423388680-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FV7OrHgKXA0t1jankQBYf%2Fuploads%2Fv8752wKRLWDtbNiDMFqj%2FEnginsight-EN-Hosts-Add%20Policy-Available%20Settings.jpg?alt=media&amp;token=1e909d23-14be-4274-932d-9c4a8bf1ddfd" alt="" width="563"><figcaption></figcaption></figure></div>

The following settings are available:

* [Enginsight Intrusion Detection System (IDS)](#enginsight-intrusion-detection-system-ids)
* [Enginsight Shield (IPS)](#enginsight-shield-ips)
* [Plugins](#plugins)
* [File Integrity Monitoring](#file-integrity-monitoring)
* [Advanced Settings](#advanced-settings)
* [Automatic OS Updates](#automatic-os-updates)
* [Tray](#tray)
* [Advanced Persistent Threats](#advanced-persistent-threats)
* [SIEM Integration](#siem-integration)

### Enginsight Intrusion Detection System (IDS)

<i class="fa-computer-mouse">:computer-mouse:</i> Click the **Add New Setting** field to expand all settings that are available for the respective section. Select a setting to add it to the settings list for that section.

{% hint style="info" %}
Added settings are enabled by default. To disable a setting, deselct the checkbox <i class="fa-square-check">:square-check:</i> next to the respective setting.
{% endhint %}

<figure><img src="https://2423388680-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FV7OrHgKXA0t1jankQBYf%2Fuploads%2FUomN5uaZdWSxdDbeZAbt%2FEnginsight-EN-Hosts-Add%20Policy-IDS.jpg?alt=media&amp;token=9f54e22f-4919-486f-9921-d8a60c7bf8c7" alt=""><figcaption></figcaption></figure>

The following options are available:

<table><thead><tr><th width="199.6328125">Option</th><th>Description</th></tr></thead><tbody><tr><td>Enabled</td><td>Allow the analysis of network traffic on assigned hosts to detect potential attacks using the <a href="/docs/manual/english/platform-usage/hosts/intrusion-detection-system.md">Enginsight Intrusion Detection System</a>.</td></tr><tr><td>IP Anonymization</td><td><p>Enable the anonymization of all IP addresses that are detected during attack detection. Anonymized IP addresses are shown in the user interface using asterisks (***).</p><div data-gb-custom-block data-tag="hint" data-style="danger" class="hint hint-danger"><p><strong>Please note:</strong> Enabling IP address anonymization limits platform functionality. For example, IP addresses can no longer be geolocated, blocked, or added to the whitelist.</p></div></td></tr><tr><td>Detection Level of Intrusion Detection System </td><td><p>Define the IDS detection level to either increase the number of detected threats or prioritize system performance by focusing only on the most important threats.<br><br><img src="https://2423388680-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FV7OrHgKXA0t1jankQBYf%2Fuploads%2FPctCj4CcJb79ZjAH60ix%2FEnginsight-EN-Hosts-Add%20Policy-IDS-Blocking%20Level.jpg?alt=media&amp;token=f9e70251-5c8e-4a2b-bba3-6aeed3b68565" alt=""><br><br>The following levels are available:</p><ul><li><strong>Level 0 (Maximum Performance)</strong>: Significantly reduces detection capabilities to maximize device performance.</li><li><p><strong>Level 1 (Performance over Security)</strong>: Detects the most important threats while prioritizing device performance.</p><div data-gb-custom-block data-tag="hint" data-style="info" class="hint hint-info"><p>We recommend <strong>Level 1</strong> for clients and heavily loaded servers.</p></div></li><li><p><strong>Level 2 (Balanced Performance and Security)</strong>: Detects more complex threats while maintaining a balance between detection quality and resource consumption.</p><div data-gb-custom-block data-tag="hint" data-style="info" class="hint hint-info"><p>We recommend <strong>Level 2</strong> for normally utilized servers.</p></div></li><li><p><strong>Level 3 (Security over Performance)</strong>: Detects rare and highly specific threats but may impact system performance.</p><div data-gb-custom-block data-tag="hint" data-style="warning" class="hint hint-warning"><p>We recommend <strong>Level 3</strong> for particularly sensitive hosts or network segments.</p></div></li><li><p><strong>Level 4 (Maximum Protection)</strong>: Detects all types of threats but can significantly impact device performance.</p><div data-gb-custom-block data-tag="hint" data-style="danger" class="hint hint-danger"><p>We recommend <strong>Level 4</strong> only in exceptional cases or for temporary use.</p></div></li></ul></td></tr><tr><td>TLS Interception</td><td><p>Allow encrypted network traffic on the host to be decrypted and analyzed to detect potential attacks.</p><div data-gb-custom-block data-tag="hint" data-style="warning" class="hint hint-warning"><p><strong>Please note</strong>: The TLS Interception feature is only supported on Linux hosts.</p></div></td></tr></tbody></table>

<i class="fa-computer-mouse">:computer-mouse:</i> Click the **Delete** icon <i class="fa-trash">:trash:</i> at the end of an option field to remove the respective setting from the settings list.

### Enginsight Shield (IPS)

<i class="fa-computer-mouse">:computer-mouse:</i> Click the **Add New Setting** field to expand all settings that are available for the respective section. Select a setting to add it to the settings list for that section.

{% hint style="info" %}
Added settings are enabled by default. To disable a setting, deselct the checkbox <i class="fa-square-check">:square-check:</i> next to the respective setting.
{% endhint %}

<figure><img src="https://2423388680-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FV7OrHgKXA0t1jankQBYf%2Fuploads%2FTuU6Z6wrA39nRrDUgo6m%2FEnginsight-EN-Hosts-Add%20Policy-IPS.jpg?alt=media&amp;token=1f5611c5-59ad-4e2c-b31c-ebcaec6f1fe7" alt=""><figcaption></figcaption></figure>

The following options are available:

<table><thead><tr><th width="199.71484375">Option</th><th>Description</th></tr></thead><tbody><tr><td>Enabled</td><td>Allow network connections to be blocked and network traffic to be restricted on assigned hosts to prevent attacks using the Enginsight Intrusion Prevention System (<a href="/docs/manual/english/platform-usage/shield.md">Shield</a>).</td></tr></tbody></table>

<i class="fa-computer-mouse">:computer-mouse:</i> Click the **Delete** icon <i class="fa-trash">:trash:</i> at the end of an option field to remove the respective setting from the settings list.

### Plugins

<i class="fa-computer-mouse">:computer-mouse:</i> Click the **Add New Setting** field to expand all settings that are available for the respective section. Select a setting to add it to the settings list for that section.

{% hint style="info" %}
Added settings are enabled by default. To disable a setting, deselct the checkbox <i class="fa-square-check">:square-check:</i> next to the respective setting.
{% endhint %}

<figure><img src="https://2423388680-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FV7OrHgKXA0t1jankQBYf%2Fuploads%2FsnNw6c8ejdmvaaRAzfrh%2FEnginsight-EN-Hosts-Add%20Policy-Plugins.jpg?alt=media&amp;token=e86c531f-bc1a-442b-89b7-19f21d08dafb" alt=""><figcaption></figcaption></figure>

The following options are available:

<table><thead><tr><th width="199.52734375">Option</th><th>Description</th></tr></thead><tbody><tr><td>Enabled</td><td>Allow assigned hosts to execute custom scripts (<a href="/docs/manual/english/platform-usage/hosts/management/plugins.md">plugins</a>).</td></tr><tr><td>Unprivileged Plugin Execution</td><td><p>Allow the host to run custom scripts in unprivileged mode, meaning without administrator privileges on Windows or root privileges on Linux. To do this, corresponding accounts with limited permissions are created on the host.</p><div data-gb-custom-block data-tag="hint" data-style="success" data-icon="lightbulb" class="hint hint-success"><p>For more information on how plugin execution in unprivileged mode works, see our Knowledge Base: <a href="https://docs.enginsight.com/docs/knowledge-base/english/plugins/how-can-i-run-plugins-in-unprivileged-mode-in-enginsight">How can I execute plugins in unprivileged mode in Enginsight?</a></p></div></td></tr></tbody></table>

<i class="fa-computer-mouse">:computer-mouse:</i> Click the **Delete** icon <i class="fa-trash">:trash:</i> at the end of an option field to remove the respective setting from the settings list.

### File Integrity Monitoring

<i class="fa-computer-mouse">:computer-mouse:</i> Click the **Add New Setting** field to expand all settings that are available for the respective section. Select a setting to add it to the settings list for that section.

{% hint style="info" %}
Added settings are enabled by default. To disable a setting, deselct the checkbox <i class="fa-square-check">:square-check:</i> next to the respective setting.
{% endhint %}

<figure><img src="https://2423388680-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FV7OrHgKXA0t1jankQBYf%2Fuploads%2F2tROpV6HrW3GtZDgXRnk%2FEnginsight-EN-Hosts-Add%20Policy-FIM.jpg?alt=media&amp;token=2f55c6d7-e8d6-435a-aaa0-f8290e2b5b80" alt=""><figcaption></figcaption></figure>

The following options are available:

<table><thead><tr><th width="199.6171875">Option</th><th>Description</th></tr></thead><tbody><tr><td>Enabled</td><td>Allow monitoring of the integrity of files and directories (<a href="/docs/manual/english/platform-usage/hosts/file-integrity-monitoring.md">File Integrity Monitoring</a>) on assigned hosts.</td></tr></tbody></table>

<i class="fa-computer-mouse">:computer-mouse:</i> Click the **Delete** icon <i class="fa-trash">:trash:</i> at the end of an option field to remove the respective setting from the settings list.

### Advanced Settings

<i class="fa-computer-mouse">:computer-mouse:</i> Click the **Add New Setting** field to expand all settings that are available for the respective section. Select a setting to add it to the settings list for that section.

{% hint style="info" %}
Added settings are enabled by default. To disable a setting, deselct the checkbox <i class="fa-square-check">:square-check:</i> next to the respective setting.
{% endhint %}

<figure><img src="https://2423388680-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FV7OrHgKXA0t1jankQBYf%2Fuploads%2Fj10iEaJEZj7ocRpcFAhM%2FEnginsight-EN-Hosts-Add%20Policy-Advanced%20Settings.jpg?alt=media&amp;token=949b47cc-9fb5-4550-9ec0-d0cc57c6f88a" alt=""><figcaption></figcaption></figure>

The following options are available:

<table><thead><tr><th width="249.9453125">Option</th><th>Description</th></tr></thead><tbody><tr><td>Recording of Security-Relevant Events</td><td>Allow a Pulsar that is installed on an assigned host to access logs and record security-relevant events.</td></tr><tr><td>Software Monitoring Using User Profiles</td><td><p>Allow a Pulsar that is installed on an assigned host to use user profiles for monitoring and inventorying software applications.<br></p><p>If this option is <em>not</em> enabled, only software that is installed system-wide and therefore available to all users on the system is searched for by default. If this option is enabled, software that is installed only for users logged in to the system is also searched for.</p><div data-gb-custom-block data-tag="hint" data-style="warning" class="hint hint-warning"><p><strong>Please note</strong>: In rare cases, using user profiles for software monitoring might result in the detection of outdated software. This can happen, for example, with user profiles that are still listed in the registry even though the user no longer exists.</p></div></td></tr><tr><td>Extended Software Monitoring</td><td><p>Allow a Pulsar installed on an assigned Windows host to scan files and directories on the system drive (C:\) every 24 hours to discover and inventory newly installed software.</p><div data-gb-custom-block data-tag="hint" data-style="warning" class="hint hint-warning"><p><strong>Please note</strong>: This option only applies to Windows hosts.</p></div></td></tr><tr><td>Extended Software Monitoring on All Disks</td><td><p>Allow a Pulsar installed on an assigned Windows host to scan files and directories on all drives of the host every 24 hours to discover and inventory installed software.</p><div data-gb-custom-block data-tag="hint" data-style="warning" class="hint hint-warning"><p><strong>Please note</strong>: This option only applies to Windows hosts. If this option is disabled, only the system drive (C:\) is monitored by default.</p></div></td></tr><tr><td>Extended Service Monitoring</td><td><p>Enable monitoring of all services that run on the assigned hosts.</p><div data-gb-custom-block data-tag="hint" data-style="warning" class="hint hint-warning"><p><strong>Please note</strong>: If this option is disabled, only services that start automatically are monitored by default.</p></div></td></tr><tr><td>Exception Lists: Services</td><td><p>Exclude specific services that run on the assigned host from monitoring. This is particularly useful for services that are started only occasionally and are not system relevant, such as the <em>Trustedinstaller</em> or <em>Mapsbroker</em> services on Windows systems.</p><div data-gb-custom-block data-tag="hint" data-style="info" class="hint hint-info"><p>We recommend that you create separate policy managers with exclusion lists for Windows clients and Windows servers, as the services used can differ.</p></div><p>Enter the name or names of the corresponding services.</p><div data-gb-custom-block data-tag="hint" data-style="info" class="hint hint-info"><p>You can use wildcards (*) here.</p></div><div data-gb-custom-block data-tag="hint" data-style="warning" class="hint hint-warning"><p><strong>Please note</strong>: Excluded services are also not taken into account when generating alarms.</p></div><p><i class="fa-computer-mouse">:computer-mouse:</i> Click the <strong>Remove</strong> icon <i class="fa-circle-xmark">:circle-xmark:</i> next to an entry to remove it from the <strong>Exception Lists: Services</strong> field.</p></td></tr><tr><td>Exception Lists: Connections</td><td><p>Exclude specific connections to the assigned host from monitoring. This can be useful if software that is actually considered trusted regularly opens and closes ports, triggering false alarms.<br><br>Enter the name or names of the connections.</p><div data-gb-custom-block data-tag="hint" data-style="info" class="hint hint-info"><p>You can use wildcards (*) here.</p></div><p><i class="fa-computer-mouse">:computer-mouse:</i> Click the <strong>Remove</strong> icon <i class="fa-circle-xmark">:circle-xmark:</i> next to an entry to remove it from the <strong>Exception Lists: Connections</strong> field.</p></td></tr><tr><td>Exception Lists: Disks</td><td><p>Exclude specific drives on the assigned host from monitoring. To do this, enter the drive path.</p><div data-gb-custom-block data-tag="hint" data-style="info" class="hint hint-info"><p>You can use wildcards (*) here.</p></div><div data-gb-custom-block data-tag="hint" data-style="warning" class="hint hint-warning"><p><strong>Please note</strong>: Excluded drives are also not taken into account when generating alarms.</p></div><p><i class="fa-computer-mouse">:computer-mouse:</i> Click the <strong>Remove</strong> icon <i class="fa-circle-xmark">:circle-xmark:</i> next to an entry to remove it from the <strong>Exception Lists: Drives</strong> field.</p></td></tr><tr><td>Customize API URL</td><td>Set a different API URL to which a Pulsar installed on an assigned host should send its results.</td></tr></tbody></table>

<i class="fa-computer-mouse">:computer-mouse:</i> Click the **Delete** icon <i class="fa-trash">:trash:</i> at the end of an option field to remove the respective setting from the settings list.

### Automatic OS Updates

<i class="fa-computer-mouse">:computer-mouse:</i> Click the **Add New Setting** field to expand all settings that are available for the respective section. Select a setting to add it to the settings list for that section.

{% hint style="info" %}
Added settings are enabled by default. To disable a setting, deselct the checkbox <i class="fa-square-check">:square-check:</i> next to the respective setting.
{% endhint %}

<figure><img src="https://2423388680-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FV7OrHgKXA0t1jankQBYf%2Fuploads%2F7VSq9YljuXolPiyKzBpF%2FEnginsight-EN-Hosts-Add%20Policy-OS%20Updates.jpg?alt=media&amp;token=4d667886-7e27-4393-a504-27ac8e4b0f82" alt=""><figcaption></figcaption></figure>

The following options are available:

<table><thead><tr><th width="250.4765625">Option</th><th>Description</th></tr></thead><tbody><tr><td>Enabled</td><td>Allow the automatic installation of all operating system updates available for operating systems that run on assigned hosts, provided Enginsight has access to them. This also includes feature updates.<br><br>You can find an overview of the update sources and update types supported by Enginsight in the chapter <a href="/docs/manual/english/platform-usage/hosts/vulnerability-management/update-manager.md">Update Manager</a>. </td></tr><tr><td>Only Security-Relevant Updates</td><td>Enable the automatic installation of only security-relevant updates for operating systems that run on the assigned hosts. With this option, feature updates are not installed automatically.</td></tr><tr><td>Restart the System After the Update</td><td>Allow assigned hosts to be restarted automatically if an installed operating system update requires a reboot.</td></tr><tr><td>OS Update Schedule</td><td>Define a schedule for the automatic installation of operating system updates using the time interval selection (see below).</td></tr><tr><td>OS Update Time Zone</td><td><p>Define the time zone used for automatic operating system updates.</p><p><br><i class="fa-computer-mouse">:computer-mouse:</i> Click the <strong>Time Zone</strong> field to show a list of all available time zones and select a time zone.</p><div data-gb-custom-block data-tag="hint" data-style="info" class="hint hint-info"><p>The default time zone is <strong>Coordinated Universal Time (UTC)</strong></p></div></td></tr><tr><td>Updates to Exclude</td><td>Define one or more software applications that should be excluded from automatic updates. </td></tr></tbody></table>

<i class="fa-computer-mouse">:computer-mouse:</i> Click the **Delete** icon <i class="fa-trash">:trash:</i> at the end of an option field to remove the respective setting from the settings list.

<div align="left"><figure><img src="https://2423388680-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FV7OrHgKXA0t1jankQBYf%2Fuploads%2FRsieOenWTuTSSsvDverr%2FEnginsight-EN-SIEM-Time%20Interval%20Selection.jpg?alt=media&amp;token=12622f35-614f-484b-b6c7-68e059b43e9d" alt="" width="527"><figcaption></figcaption></figure></div>

The following options are available:

<table><thead><tr><th width="199.9140625">Option</th><th>Description</th></tr></thead><tbody><tr><td>Time Zone</td><td><p>Define the time zone that you want to use for the selected time interval.</p><p></p><p><i class="fa-computer-mouse">:computer-mouse:</i> Click the <strong>Time Zone</strong> field to expand a list of all available time zones, and select a time zone.</p></td></tr><tr><td>Cron Expression (Vixie/Unix)</td><td>Shows the defined interval as a cron expression. The cron expression is updated automatically whenever you configure a time interval manually.<br><br><i class="fa-computer-mouse">:computer-mouse:</i> Click the <strong>Cron Expression</strong> field to <a href="/docs/manual/english/appendix/angabe-von-cron-ausdruecken.md">edit the cron expression manually</a>.</td></tr><tr><td>Next Execution (Local Time Zone)</td><td>Shows the exact date and time of the next execution in your <em>browser’s local time zone</em>.</td></tr><tr><td>Description</td><td>Shows the defined interval for recurring execution as a plain-language description.</td></tr><tr><td>Time Interval Selection</td><td><p>Define a custom execution interval.</p><p><br>Select the relevant minutes, hours, days of the month, months, or days of the week.</p></td></tr></tbody></table>

### Tray

<i class="fa-computer-mouse">:computer-mouse:</i> Click the **Add New Setting** field to expand all settings that are available for the respective section. Select a setting to add it to the settings list for that section.

{% hint style="info" %}
Added settings are enabled by default. To disable a setting, deselct the checkbox <i class="fa-square-check">:square-check:</i> next to the respective setting.
{% endhint %}

<figure><img src="https://2423388680-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FV7OrHgKXA0t1jankQBYf%2Fuploads%2FpU22yEr0P9rc71aYnqHs%2FEnginsight-EN-Hosts-Add%20Policy-Tray.jpg?alt=media&amp;token=caab819f-535c-43c0-bede-9f42c57891a8" alt=""><figcaption></figcaption></figure>

The following options are available:

<table><thead><tr><th width="199.92578125">Option</th><th>Description</th></tr></thead><tbody><tr><td>Enable Enginsight Tray Icon</td><td><p>Enable the Enginsight tray icon <img src="https://content.gitbook.com/content/V7OrHgKXA0t1jankQBYf/blobs/qogYWecqSJp1n0U5kl6r/Enginsight-Einstellungen-Tray%20Icon.jpg" alt=""> on the desktop of assigned hosts.</p><p><br><i class="fa-computer-mouse">:computer-mouse:</i> Click the tray icon on the host desktop to open the tray menu.<br><br>The tray menu shows the installed Pulsar version and allows <strong>Notifications</strong> to be enabled or disabled directly.</p></td></tr><tr><td>Show Notifications</td><td>Enable the display of notifications from the Enginsight platform on the desktop of assigned hosts.</td></tr></tbody></table>

<i class="fa-computer-mouse">:computer-mouse:</i> Click the **Delete** icon <i class="fa-trash">:trash:</i> at the end of an option field to remove the respective setting from the settings list.

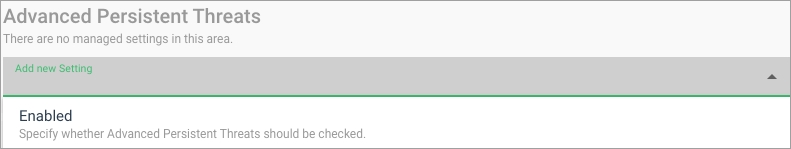
### Advanced Persistent Threats

<i class="fa-computer-mouse">:computer-mouse:</i> Click the **Add New Setting** field to expand all settings that are available for the respective section. Select a setting to add it to the settings list for that section.

{% hint style="info" %}
Added settings are enabled by default. To disable a setting, deselct the checkbox <i class="fa-square-check">:square-check:</i> next to the respective setting.
{% endhint %}

<figure><img src="https://2423388680-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FV7OrHgKXA0t1jankQBYf%2Fuploads%2FB4xtyv94t8mqx0P8U4DB%2FEnginsight-EN-Hosts-Add%20Policy-APT.jpg?alt=media&amp;token=b71d6b55-b03f-4ddb-98d9-6ebd5a0a1728" alt=""><figcaption></figcaption></figure>

The following options are available:

<table><thead><tr><th width="199.8203125">Option</th><th>Description</th></tr></thead><tbody><tr><td>Enabled</td><td>Allow assigned hosts to be scanned for <a href="/docs/manual/english/platform-usage/hosts/advanced-persistent-threats.md">Advanced Persistent Threats</a>.</td></tr></tbody></table>

<i class="fa-computer-mouse">:computer-mouse:</i> Click the **Delete** icon <i class="fa-trash">:trash:</i> at the end of an option field to remove the respective setting from the settings list.

### SIEM-Integration

<i class="fa-computer-mouse">:computer-mouse:</i> Click the **Add New Setting** field to expand all settings that are available for the respective section. Select a setting to add it to the settings list for that section.

{% hint style="info" %}
Added settings are enabled by default. To disable a setting, deselct the checkbox <i class="fa-square-check">:square-check:</i> next to the respective setting.
{% endhint %}

<figure><img src="https://2423388680-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FV7OrHgKXA0t1jankQBYf%2Fuploads%2FYIS3k6A7PBAQ4oKE5Kus%2FEnginsight-EN-Hosts-Add%20Policy-SIEM.jpg?alt=media&amp;token=e3957af9-6bb2-4262-a6bf-4e81406a0262" alt=""><figcaption></figcaption></figure>

The following options are available:

<table><thead><tr><th width="199.8203125">Option</th><th>Description</th></tr></thead><tbody><tr><td>Enabled</td><td>Allows the Pulsar installed on assigned hosts to send information to the <a href="/docs/manual/english/platform-usage/siem.md">Enginsight SIEM</a>.</td></tr></tbody></table>

<i class="fa-computer-mouse">:computer-mouse:</i> Click the **Delete** icon <i class="fa-trash">:trash:</i> at the end of an option field to remove the respective setting from the settings list.

***

## Importing Policy Managers

<i class="fa-computer-mouse">:computer-mouse:</i> Click <i class="fa-plus">:plus:</i> **Create Policy** in the upper-right corner of the [policy manager overview](/docs/manual/english/platform-usage/hosts/management/policy-manager.md#policy-manager-overview) and select <i class="fa-arrow-down-to-square">:arrow-down-to-square:</i> **Import** from the submenu that opens to import policy managers.

The **Import Policy Manager** window opens.

<div align="left"><figure><img src="https://2423388680-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FV7OrHgKXA0t1jankQBYf%2Fuploads%2F9QhYmTxLjyVDDOdTfyE7%2FEnginsight-EN-Hosts-Add%20Policy-Import-1.jpg?alt=media&amp;token=f96cbc0a-1ba4-4d31-b10a-c4deef5b76ec" alt="" width="411"><figcaption></figcaption></figure></div>

<i class="fa-computer-mouse">:computer-mouse:</i> Click in the window to select a ZIP file from your device that contains the objects intended for import. Alternatively, drag and drop a ZIP file into the window to validate it and prepare it for import.

After validation, you will see whether the file to be imported matches the expected format and how many objects can be imported.&#x20;

<div align="left"><figure><img src="https://2423388680-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FV7OrHgKXA0t1jankQBYf%2Fuploads%2FrAZi7ZX7ju5Kh0o23o45%2FEnginsight-EN-Hosts-Add%20Policy-Import-2.jpg?alt=media&amp;token=7142fea0-943e-404a-9d1d-276109d6ec83" alt="" width="410"><figcaption></figcaption></figure></div>

The following import options are also available:

<table><thead><tr><th width="172.6015625">Option</th><th>Description</th></tr></thead><tbody><tr><td>Create New</td><td>Select this option to create each imported policy manager as a new entry.</td></tr><tr><td>Update</td><td>Select this option to update existing policy managers during import. All other imported policy managers are created as new entries.</td></tr><tr><td>Skip</td><td><p>Select this option to skip all existing policy managers during import. All other imported policy managers are created as new entries.</p><div data-gb-custom-block data-tag="hint" data-style="info" class="hint hint-info"><p>This option is selected by default.</p></div></td></tr></tbody></table>

<i class="fa-computer-mouse">:computer-mouse:</i> Click **Import** to start importing the file. After a successful import, you can find the added policy managers in the [policy manager overview](/docs/manual/english/platform-usage/hosts/management/policy-manager.md#policy-manager-overview).

<i class="fa-computer-mouse">:computer-mouse:</i> Click **Cancel** to return to the list overview.

***

## Further Resources

**Knowledge Base**

* [How can I execute plugins in unprivileged mode in Enginsight?](https://docs.enginsight.com/docs/knowledge-base/english/plugins/how-can-i-run-plugins-in-unprivileged-mode-in-enginsight)

***